AI & TechnologyNovember 16, 2026
How to Build a Secure CI/CD Pipeline: A Step-by-Step Guide
A stage-by-stage blueprint for a secure CI/CD pipeline, mapped to the OWASP Top 10 CI/CD Security Risks, with the controls to add first and a rollout order.
Agix International
Agix International
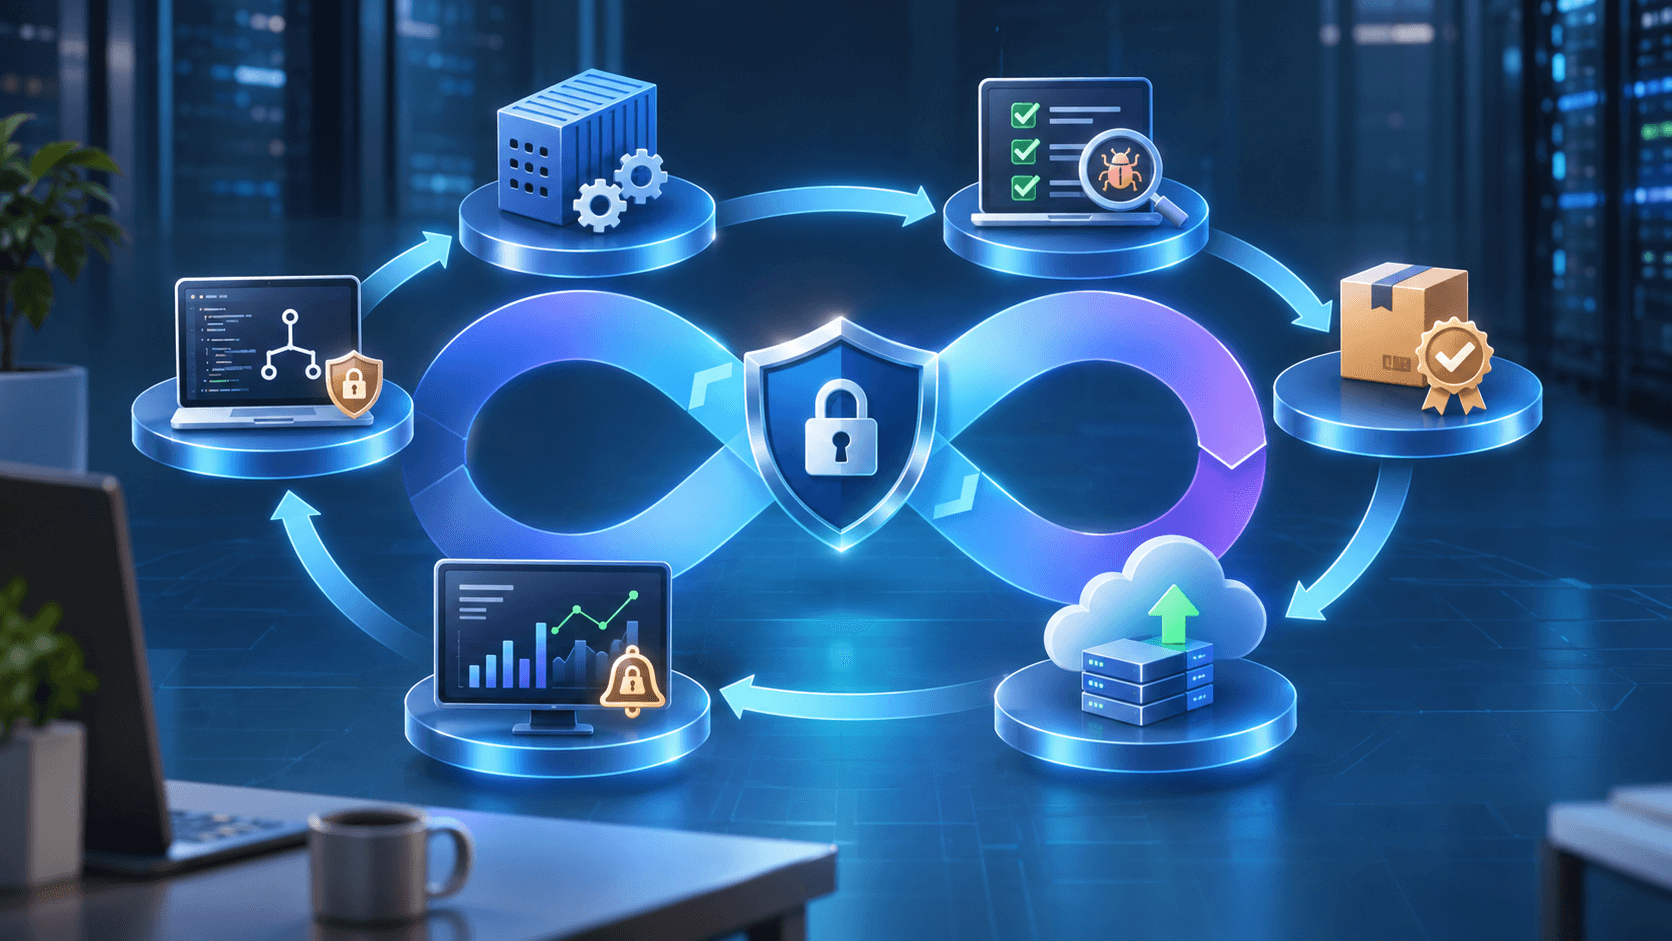
How to Build a Secure CI/CD Pipeline: A Step-by-Step Blueprint
A secure CI/CD pipeline does two jobs: it checks the code it ships, and it protects itself from being used as an attack path. In practice, that means protected branches and reviews, short-lived credentials, isolated build runners, security scans that block only high-confidence risks, signed artifacts, and logs of everything the pipeline does.
Many security conversations about pipelines focus on what the pipeline scans: code, dependencies, containers. That matters. But the pipeline is also one of the most privileged systems in any engineering organization. It holds cloud credentials, signing keys, and the ability to deploy to production. An attacker who controls it does not need to break into production; the pipeline will deploy their code for them.
This blueprint covers both sides. It is part of our DevSecOps guide, and it assumes you have read why DevSecOps differs from DevOps.
The Threat Model: OWASP Top 10 CI/CD Security Risks
The OWASP Top 10 CI/CD Security Risks is a useful starting point for pipeline threat modeling. The ten risks are:
| ID | Risk | What it means in practice |
|---|---|---|
| CICD-SEC-1 | Insufficient Flow Control Mechanisms | Code can reach production without review or approval |
| CICD-SEC-2 | Inadequate Identity and Access Management | Too many people and service accounts have too much access |
| CICD-SEC-3 | Dependency Chain Abuse | Malicious or confused packages enter the build |
| CICD-SEC-4 | Poisoned Pipeline Execution (PPE) | An attacker changes pipeline steps by modifying code or configuration |
| CICD-SEC-5 | Insufficient PBAC (Pipeline-Based Access Controls) | Pipeline jobs can reach secrets and systems they do not need |
| CICD-SEC-6 | Insufficient Credential Hygiene | Secrets are hardcoded, long-lived, or exposed in logs |
| CICD-SEC-7 | Insecure System Configuration | CI servers and runners are misconfigured or unpatched |
| CICD-SEC-8 | Ungoverned Usage of 3rd Party Services | Third-party apps and plug-ins get broad access unchecked |
| CICD-SEC-9 | Improper Artifact Integrity Validation | Nobody verifies that what is deployed is what was built |
| CICD-SEC-10 | Insufficient Logging and Visibility | Pipeline activity cannot be investigated after an incident |
The blueprint below is organized by pipeline stage, with the relevant risks noted for each.
Stage 1: Source Control
Risks addressed: CICD-SEC-1, CICD-SEC-2, CICD-SEC-4
- Protect the main branch: require pull requests, at least one independent review, and passing checks before merge.
- Require review for changes to pipeline definitions, build scripts, and infrastructure code, ideally by a designated owner.
- Enforce multifactor authentication for everyone with write access.
- Remove inactive accounts and review repository permissions regularly.
- Be careful with workflows triggered by pull requests from forks. Untrusted code should never run with access to secrets.
Stage 2: Build
Risks addressed: CICD-SEC-3, CICD-SEC-5, CICD-SEC-7
- Run builds on isolated, ephemeral runners that are destroyed after each job, so one build cannot tamper with the next.
- Give each job only the permissions and secrets it needs. A unit test job does not need production deploy credentials.
- Pull dependencies through a controlled registry or proxy, and pin versions with lock files.
- Pin third-party actions and plug-ins to a specific version or commit hash rather than a moving tag.
- Generate a software bill of materials during the build. Our SBOM guide explains formats and storage.
Stage 3: Test and Scan
Risks addressed: CICD-SEC-3, CICD-SEC-6
- Scan every commit for hardcoded secrets, and block the merge if one is found.
- Run software composition analysis on dependencies and static analysis on source code.
- Run dynamic tests against a deployed test environment.
- Block only on high-confidence, high-impact findings, and route the rest to the owning team with a deadline.
Which scanner catches what is often misunderstood. We compare them in SAST vs. DAST vs. IAST vs. SCA, and explain how to keep findings manageable in our article on shift-left security.
Stage 4: Package and Sign
Risks addressed: CICD-SEC-9
- Push built artifacts to a private registry, never directly from a developer machine.
- Sign artifacts and container images, for example with Sigstore cosign, and record build provenance.
- Store the SBOM and provenance alongside the artifact they describe.
Stage 5: Deploy
Risks addressed: CICD-SEC-5, CICD-SEC-6, CICD-SEC-9
- Replace long-lived cloud keys with short-lived credentials issued through OpenID Connect (OIDC) federation between your CI platform and your cloud provider.
- Verify signatures at deploy time. In Kubernetes, an admission controller such as Kyverno can reject unsigned images.
- Require manual approval for production deployments of high-risk services.
- Scan infrastructure as code before it is applied, and block policy violations such as public storage buckets.
Stage 6: Monitor and Respond
Risks addressed: CICD-SEC-8, CICD-SEC-10
- Send CI/CD audit logs, including who changed which pipeline and which job accessed which secret, to your central logging system.
- Review installed third-party apps and integrations, and remove those that are unused or overprivileged.
- Alert on unusual activity, such as pipeline changes outside working hours or new deploy targets.
- For teams in India, remember that the CERT-In Directions of April 28, 2022 require specified cyber incidents to be reported within six hours and system logs to be kept for a rolling 180 days within Indian jurisdiction. Pipeline logs are part of that evidence.
What to Do First
If you are starting from an unsecured pipeline, this order tackles the highest-risk gaps first:
- Protect main and require reviews, including for pipeline files.
- Move secrets into a vault and turn on secret scanning.
- Switch cloud access to OIDC and remove long-lived keys.
- Restrict job permissions to what each job needs.
- Pin dependencies and third-party actions.
- Add SCA and SAST in report-only mode, then block on critical findings.
- Sign artifacts and verify at deploy.
- Centralize pipeline logs.
Common Mistakes
- Treating the CI system as trusted infrastructure that does not need patching or monitoring.
- Giving every job the same set of secrets "to keep things simple."
- Running untrusted pull request code with access to deploy credentials.
- Adding many scanners in blocking mode at once, then disabling them when releases stall.
- Signing artifacts but never verifying signatures at deploy time.
Frequently Asked Questions
What Makes a CI/CD Pipeline Secure?
A secure pipeline enforces review before code reaches production, uses short-lived and narrowly scoped credentials, runs builds in isolation, scans code and dependencies, signs what it builds, and logs everything it does.
What Is Poisoned Pipeline Execution?
It is an attack in which someone changes what a pipeline runs, for example by editing a build script in a pull request, so the pipeline executes their code with its own privileges.
Why Use OIDC Instead of Cloud Access Keys in CI/CD?
OIDC lets the pipeline request short-lived credentials for each job, so there are no long-lived keys to leak or rotate.
Which Security Scans Should Block a Build?
Start by blocking exposed secrets and critical vulnerabilities that are reachable or known to be exploited. Report everything else until the team trusts the findings.
Secure Your Pipeline with Agix
Agix International builds cloud, DevOps, and cybersecurity foundations for growing businesses in India and the GCC. If you want an outside review of your pipeline and a prioritized fix list, book a consultation.